Our verdict: Tailscale is the best pick for most developers. Its free plan covers a whole homelab and setup takes minutes. Cloudflare Zero Trust is the best free plan for teams (up to 50 users), and Twingate is best for locking contractors to one service.
Every developer with a homelab hits the same wall: you want to SSH into your home server from a coffee shop without opening port 22 on your router. The fix is a mesh VPN or zero trust network, and three names lead the category: Tailscale, Cloudflare Zero Trust and Twingate.
 Tailscale
 Cloudflare Zero Trust
Twingate
How traffic flows in each
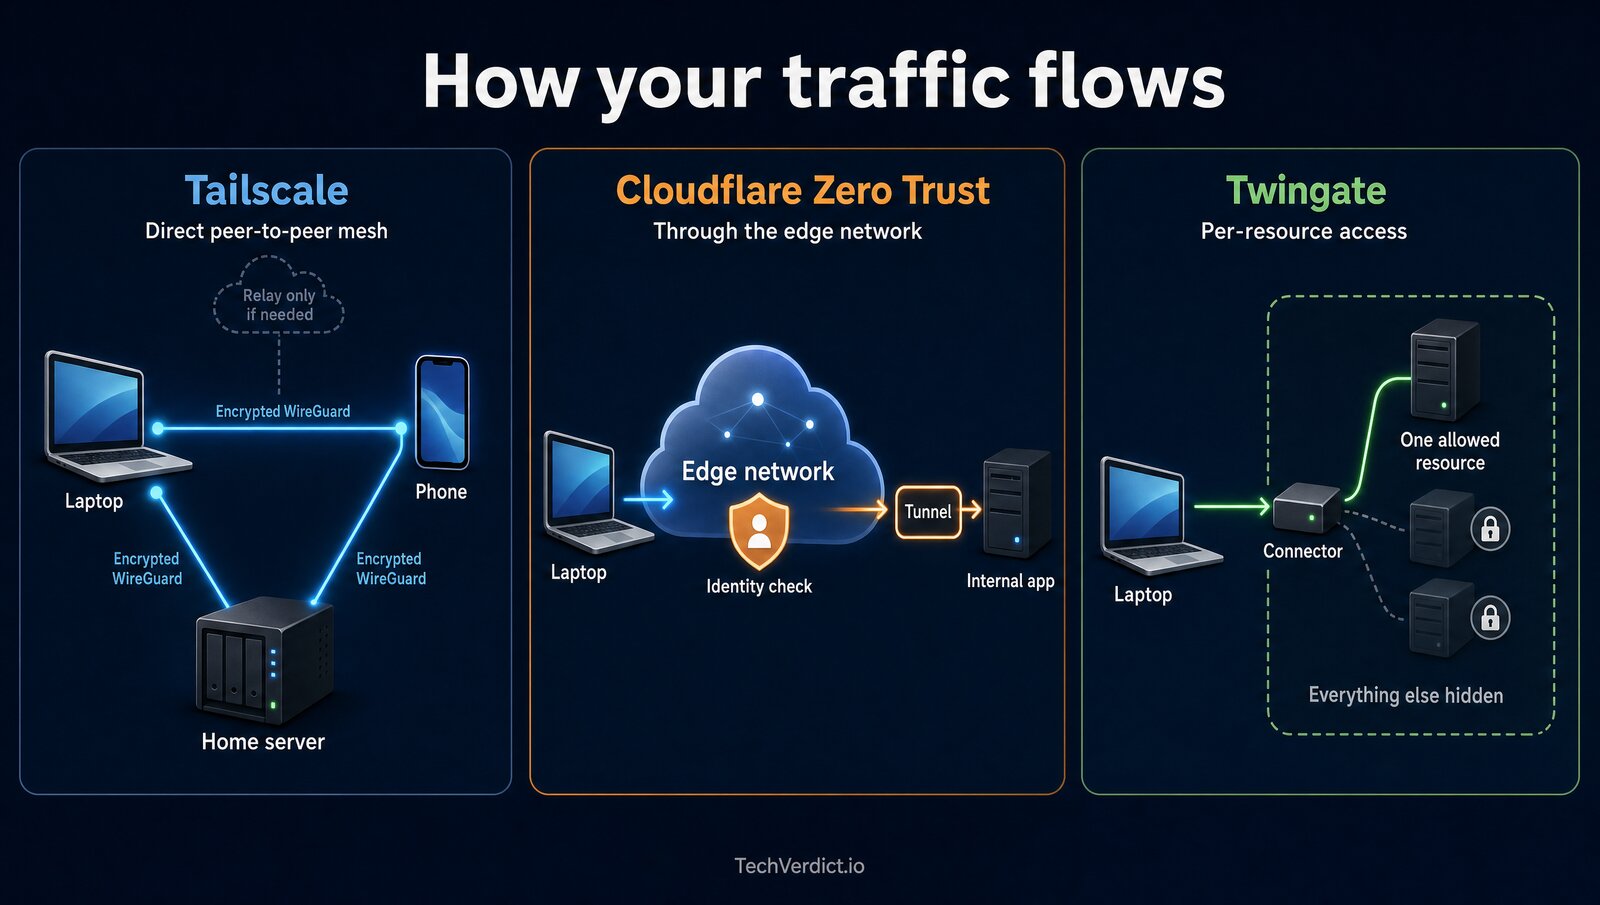
This is the real difference between them. Tailscale links your devices to each other. Cloudflare puts its network in the middle and checks who you are. Twingate hides everything except the exact service you're allowed to reach.
The 3 at a glance
Tailscale- Direct peer-to-peer WireGuard mesh
- Reach any device by name, no port forwarding
- Exit nodes and SSO on the free plan
The catch: access rules are machine-level first, so per-service rules take more work.
Cloudflare Zero Trust- Identity checked at Cloudflare's edge
- Browser access to internal apps, no client
- Central policy and logging
The catch: the slowest setup here, with tunnels and policies to configure.
- Grants access to one resource, not a network
- Connectors sit inside your network
- Cheapest paid plan per user
The catch: no device-to-device mesh, and the tightest free plan.
Prices and plans
Prices checked October 15, 2026, on each company's own pricing page.
| Service | Free plan | Paid plans | How traffic flows | Best for |
|---|---|---|---|---|
| Tailscale | Up to 6 users, unlimited personal devices | Standard $8/user/mo; Premium $18/user/mo | Peer-to-peer WireGuard mesh | Solo devs, homelabs, engineering teams |
| Cloudflare Zero Trust | Up to 50 users | Pay-as-you-go and Enterprise (no per-user price listed) | Through Cloudflare's edge network | Orgs already on Cloudflare, browser-based access |
| Twingate | Starter: up to 5 users, 5 devices each | Home $15/mo (7 users); Teams $5/user/mo; Business $10/user/mo | Per-resource connectors | Contractor and vendor access |
Feature checklist
| Feature | Tailscale | Cloudflare | Twingate |
|---|---|---|---|
| Free plan users | 6 | 50 | 5 |
| Mesh, device to device | ✓ | Via Cloudflare (Mesh) | ✗ |
| Per-app access | Port-level ACLs | ✓ | ✓ |
| Self-hostable control server | Headscale (third-party) | ✗ | ✗ |
| Exit nodes | ✓ | Via Cloudflare's network | Exit Networks, Home and Business |
| SSO sign-in | ✓ | ✓ | Teams and up |
Self-hostable means running the control server yourself. Headscale is an open-source project Tailscale supports but doesn't run.
Tailscale: the one that just works
Install it, sign in with Google or GitHub, and the device joins your tailnet. Every other device can then reach it by name, through NAT and firewalls, with no port forwarding or certificates. Under the hood it's WireGuard, with relays only when a direct link fails.
The weak spot is fine-grained access. ACLs can restrict ports, but "contractor X gets only port 5432 on database Y" gets awkward fast. Peer-to-peer traffic can also clash with rules that require central logging of everything.
Cloudflare Zero Trust: for orgs already on Cloudflare
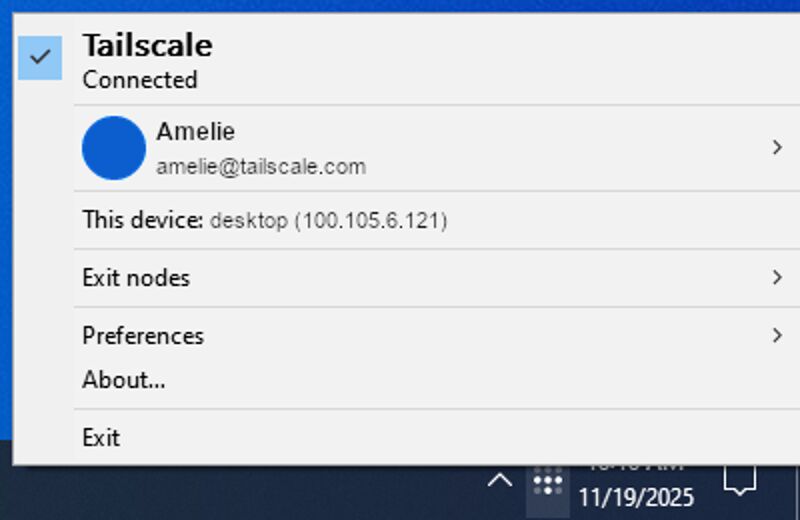
Here, traffic goes through Cloudflare's edge. Apps are exposed through Cloudflare Tunnel, and identity from Okta, Entra ID or Google Workspace is checked before anything reaches your network. You can layer the rest of Cloudflare's security tools on the same policies.
Its standout is browser-based access: a new hire opens the internal dashboard in any browser with no VPN client. The newer Cloudflare Mesh adds device-to-device links, but every packet still passes through Cloudflare rather than going direct.
TGTwingate: for fine-grained access
Twingate skips the "join the network, reach everything" model. You grant access to one resource, such as port 8080 on the staging API, and nothing else is visible. Audit logs and access reviews follow the same precise lines, and revoking is exact.
That's ideal for agencies, vendors and freelancers, but more admin than a solo developer needs. Paid plans are the cheapest per user here, at $5 on Teams versus $8 for Tailscale Standard.
Setup time, roughly
| Service | Laptop to home server SSH | What you do |
|---|---|---|
| Tailscale | About 5 minutes | Install, sign in, done |
| Twingate | About 10 minutes | Install, sign in, accept resource access |
| Cloudflare Zero Trust | About 25 minutes if new to Tunnels | Set up a tunnel, an Access policy and an identity provider |
Estimates from each company's setup steps, not timed tests.
What about raw WireGuard or OpenVPN?
You can run them yourself, and some people do. Most stop because of the upkeep: keys, NAT, client updates and config files. All three services above are WireGuard-style networking with that work removed, so roll your own only if you enjoy it.
Which one should you use?
Many growing companies run two: Tailscale for engineers reaching servers, and Cloudflare Zero Trust for everyone else reaching internal tools in a browser.
The verdict
Tailscale is the right answer for most developers in 2026, and the free plan makes the choice easy. Move to Cloudflare Zero Trust when you're already on Cloudflare or need browser-based access, and to Twingate when contractors need one service and nothing more.
FAQ
Is Tailscale still the best mesh VPN in 2026?
For solo developers, homelabs and small teams, yes. Setup is still the simplest in the category, and the free Personal plan covers up to 6 users with no device cap. Larger organizations already on Cloudflare should look hard at Cloudflare Zero Trust, which is free for up to 50 users.
How much does Tailscale cost?
The Personal plan is free for up to 6 users with unlimited devices. Standard costs $8 per user a month and Premium costs $18 per user a month. Most homelabs and solo developers never need to pay.
What's the difference between Tailscale and Cloudflare Zero Trust?
Tailscale connects your devices directly to each other, peer-to-peer over WireGuard. Cloudflare Zero Trust sends traffic through Cloudflare's edge network, which checks identity before anything reaches your apps. Tailscale is simpler; Cloudflare is stronger on central policy, logging and browser-based access.
Is Twingate worth using over Tailscale?
Yes, if you need to give contractors or vendors access to one specific service. Twingate grants access per resource, such as a single port on one server, instead of per machine. For general developer use, Tailscale's simpler model is easier to live with.
Do I need a mesh VPN if I just have a home server?
It's the safer alternative to opening ports on your home router. Install Tailscale on your laptop and your home server, sign in on both, and you can SSH in from anywhere without exposing port 22. The free plan covers it, and setup takes about 10 minutes.